Smart Edge Security
Secure, trusted access from any network
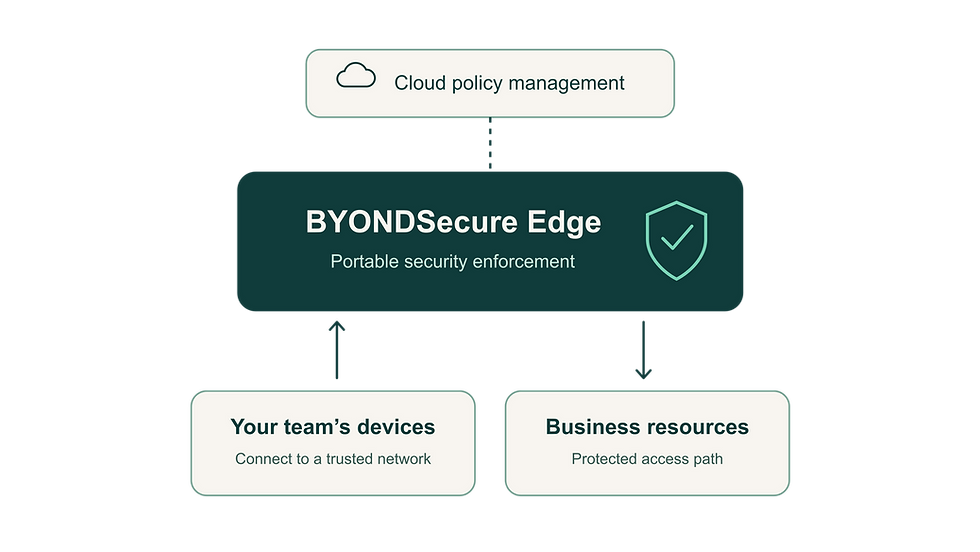
BYONDSecure adds a portable security enforcement layer between unmanaged networks and the business resources your organization depends on. Whether users connect from home, hotels, airports, branches, customer sites, or other third-party environments, BYONDSecure helps make access more trusted, policy-driven, and controlled.
What BYONDSecure Is
It pairs a portable secure device with a cloud console, so every connection gets a protected path and IT keeps visibility and control - no matter whose network people are on.
In Plain English
BYONDSecure helps make risky networks safer for work. When users connect from home, hotels, public Wi-Fi, or third-party networks, BYONDSecure adds a policy-driven security layer before access reaches business resources. It gives organizations more control over the access environment without requiring every network to be owned or managed by IT.
Integrated Security
BYONDSecure combines network awareness, secure DNS, identity context, and policy enforcement to help organizations make better access decisions at the distributed edge.
Encrypted Overlay
BYONDSecure uses encrypted overlay connectivity to help protect traffic as users move from unmanaged networks to trusted business resources.
Connectivity and Risk Beyond IT
Work happens everywhere, but access often begins on networks IT cannot inspect, configure, or trust. BYONDSecure helps close this gap by extending policy-driven security to the edge of connectivity.
Unmanaged Environments
Untrusted Network Locations
- Home offices
- Hotels and airports
- Public Wi-Fi
- Mobile hotspots
Blind Spots
Missing Visibility
- Unknown network conditions
- Limited access-path visibility
- Inconsistent policy enforcement
- Unmanaged connectivity risk
Risk Exposure
Access Risk
- Exposure on public or shared networks
- Weak control before resource access
- Risk from unmanaged environments
- Reduced confidence in access conditions
The Process
A simple four-step model for trusted access
1
Assess the Network Context
BYONDSecure evaluates the network environment where access begins, helping determine whether additional controls or policy actions are needed.
2
Set Up the Trusted Network
The device brings up your organization's own trusted network, so laptops and phones connect to it instead of untrusted local Wi-Fi.
3
Apply Policy at the Edge
Security policies are enforced closer to the user, helping organizations apply consistent controls even when access begins outside managed networks.
4
Establish a Protected Access Path
BYONDSecure helps establish an encrypted access path between the user and trusted resources, reducing exposure on unmanaged or untrusted networks.
Platform Capabilities

Distributed Edge Security
Extend security enforcement to the edge of connectivity, where unmanaged network risk begins.

Centralized Orchestration
Manage access policy centrally and distribute enforcement to BYONDSecure edge environments.

Policy-Driven Access
Apply access rules based on user, device, network, and policy conditions.
The Global Edge Security Advantage
Legacy Security
Traditional Perimeter Security
Traditional tools often assume users connect from managed environments or route traffic back through centralized control points.
BYONDSecure Edge
BYONDSecure Edge
BYONDSecure extends policy enforcement to the edge of connectivity, helping protect access wherever users connect.
Standard Tunnels
Traditional VPNs
VPNs can encrypt traffic, but they may not fully address local network risk, identity-aware policy, or visibility into unmanaged access environments.
BYOND Path
Network-Aware Access
BYONDSecure combines secure connectivity with edge enforcement, network awareness, and policy-driven access decisions.
Software Only
Endpoint-Only Tools
Endpoint tools protect the device, but they do not fully control the network environment where access begins.
Edge Enforcement
Portable Edge Enforcement
BYONDSecure adds a dedicated enforcement layer between unmanaged networks and trusted business resources.
Consumer Grade
Commodity Connectivity Devices
Basic routers and hotspots provide connectivity, but they are not designed for centralized policy orchestration or enterprise access governance.
Enterprise Edge
Enterprise Policy Platform
BYONDSecure gives organizations centralized control, distributed enforcement, and improved visibility across unmanaged access environments.
What Sets Our Platform Apart
BYONDSecure helps organizations protect access in the places traditional security does not fully reach: home offices, public networks, travel environments, contractor locations, branch sites, and other distributed environments.
Remote Workforces
Consistent Protection for Remote Work
Extend policy-driven access controls to home offices and hybrid work environments without assuming the local network is trusted.
Global Travel
Safe Access on Public Networks
Help traveling users connect from hotels, airports, conferences, and public networks with stronger access protection and reduced exposure.
Cloud Operations
Protected Cloud and SaaS Access
Apply identity-aware and policy-driven controls before users connect to SaaS, cloud, and private business resources.
Contractor Access
Isolated Third-Party Connectivity
Provide controlled access for contractors and third parties without treating their networks as trusted environments.
Centralized Control, Edge Enforcement
BYONDSecure separates policy management from policy execution. Administrators define access rules centrally, then distribute those policies to BYONDSecure edges where users connect. This helps organizations maintain consistent control while enforcing decisions closer to the network conditions that create risk.
Untrusted or Unmanaged Network
Home
Hotel
Public Wi-Fi
Branch
Customer Site
Central Policy Orchestration
BYONDSecure Edge
Trusted Resources
SaaS
Cloud Apps
Private Applications
Business Systems
Strategic Outcomes
Reduced Access Risk
Help protect access that begins outside managed enterprise networks.
More Consistent Enforcement
Apply security policy across distributed users, locations, and network conditions.
Simpler Distributed Operations
Centralize policy management while extending enforcement closer to users.
Greater Visibility Beyond the Perimeter
Improve awareness of access environments that are traditionally hard to observe.

Secure Your Distributed Edge
See how BYONDSecure can help your organization extend modern security to unmanaged networks, distributed users, and access environments beyond the traditional perimeter.